Printers, CCTV, refrigeration controllers and building systems are routinely left out of security reviews, with default credentials and unpatched firmware making them easy entry points for cybercrimals.
After a cyber attack reportedly hit French grocery chains including Carrefour, Monoprix, Intermarché and Coopérative U, Intermarché’s CEO said losses likely reached tens of millions of euros nationwide in a single day. The incident shows how quickly disruption to operational systems can turn into direct financial damage.
Cybersecurity resilience firm FLR Spectron says it points to a problem many UK organisations haven’t addressed, which is a growing number of internet-connected devices that nobody classes as “computers”, and so nobody secures. These unmanaged devices and equipment can provide a key entry point for threat actors to gain access to sensitive information or a chance to control systems internally.
The overlooked attack surface
FLR Spectron has identified the categories most often missing from company internal security reviews, including:
Office: printers and multifunction devices (which store documents and sit on the corporate network), CCTV and door access systems, VoIP phones, meeting-room equipment, routers, Wi-Fi access points, network switches, smart heating, lighting and locks, and USB devices that can carry malware
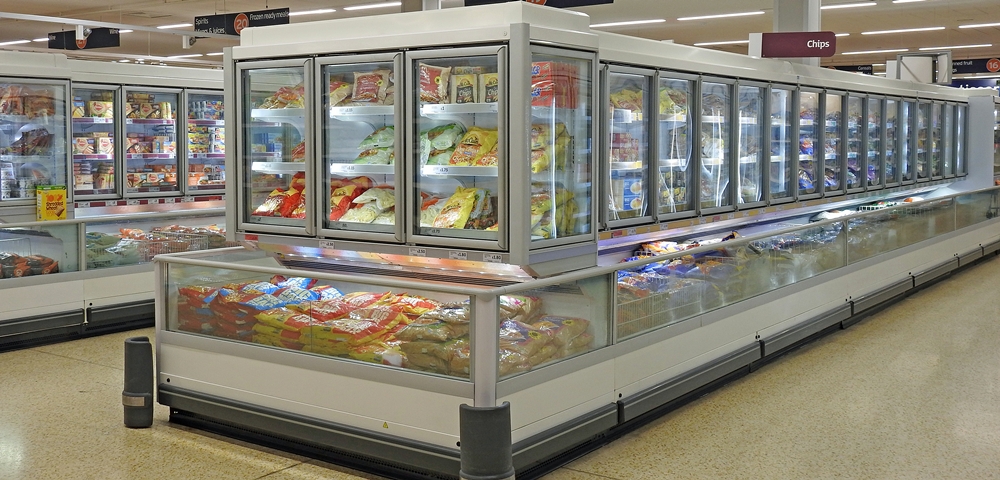
Retail, hospitality and warehousing: refrigeration and cold-storage controllers, point-of-sale terminals and card readers, and building management systems covering heating, ventilation, lighting and lifts
Why these devices are so exposed
FLR Spectron states that the above share three weaknesses that leave these systems so exposed to cyber attacks, including:
Unpatched firmware. Updates are rarely applied because the device isn’t seen as a computer, for example a refrigerator or smart heating and lighting.
Default credentials. Factory passwords often remain in place long after installation.
No ownership or visibility. Many organisations can’t say how many connected devices they have or who is responsible for them.
Once attackers compromise one of these devices, they can use it as a foothold to move laterally into the wider network.
Kamran Bahdur, Chief Technical Officer at FLR Spectron, said:
“When people think about cyber security, they picture laptops and phones, but the devices that often get overlooked are the ones nobody thinks of as computers: printers, CCTV, smart TVs, routers, even meeting-room equipment. These devices are often set up and forgotten about as they are frequently left on default passwords and rarely updated, which makes them an easy access point for cybercriminals to enter a wider network, with potentially catastrophic consequences.
“Most businesses in several different sectors couldn’t tell you exactly how many connected devices are currently on their network, and that’s the problem. Every connected device is a potential entry point, so businesses need to know what’s on their network before they can put steps into place to secure it.”
Seven steps organisations can take now
1. Build a full asset inventory, including operational equipment such as refrigeration, heating and building systems
2. Audit what’s reachable from the public internet. Operational equipment rarely needs to be.
3. Replace default passwords at installation and rotate them regularly
4. Patch promptly, including devices that don’t look like computers
5. Segment the network, keeping IoT and operational equipment separate from business-critical systems
6. Pin down supplier responsibility by asking who patches each device and how fast vulnerabilities are fixed
7. Plan for physical impact. Ask what you would do if access control failed, and how quickly you’d notice.